Services / Data security
DataWe design and operate data protection, keys, and copies
We design, deploy, and operate protection for your datasets. We start from what you hold: classes, locations, who has the key, and which RPO. Then we stand up encryption, KMS, and two copy paths. We stay for FIM, GDPR requests, retention, and a restore on the calendar.
How it fits together
From the dataset map to keys, copies, and the audit trail
First we understand the datasets and who holds the key. On that basis we put together platform encryption, backup, access detection, and a report. Proxmox Backup Server, KMS, Wazuh, and Grafana are what we use for that work every day.
- Data classification sets what goes to path B and what the retention is.
- A restore test is a calendar entry, with a report for you and for audit.
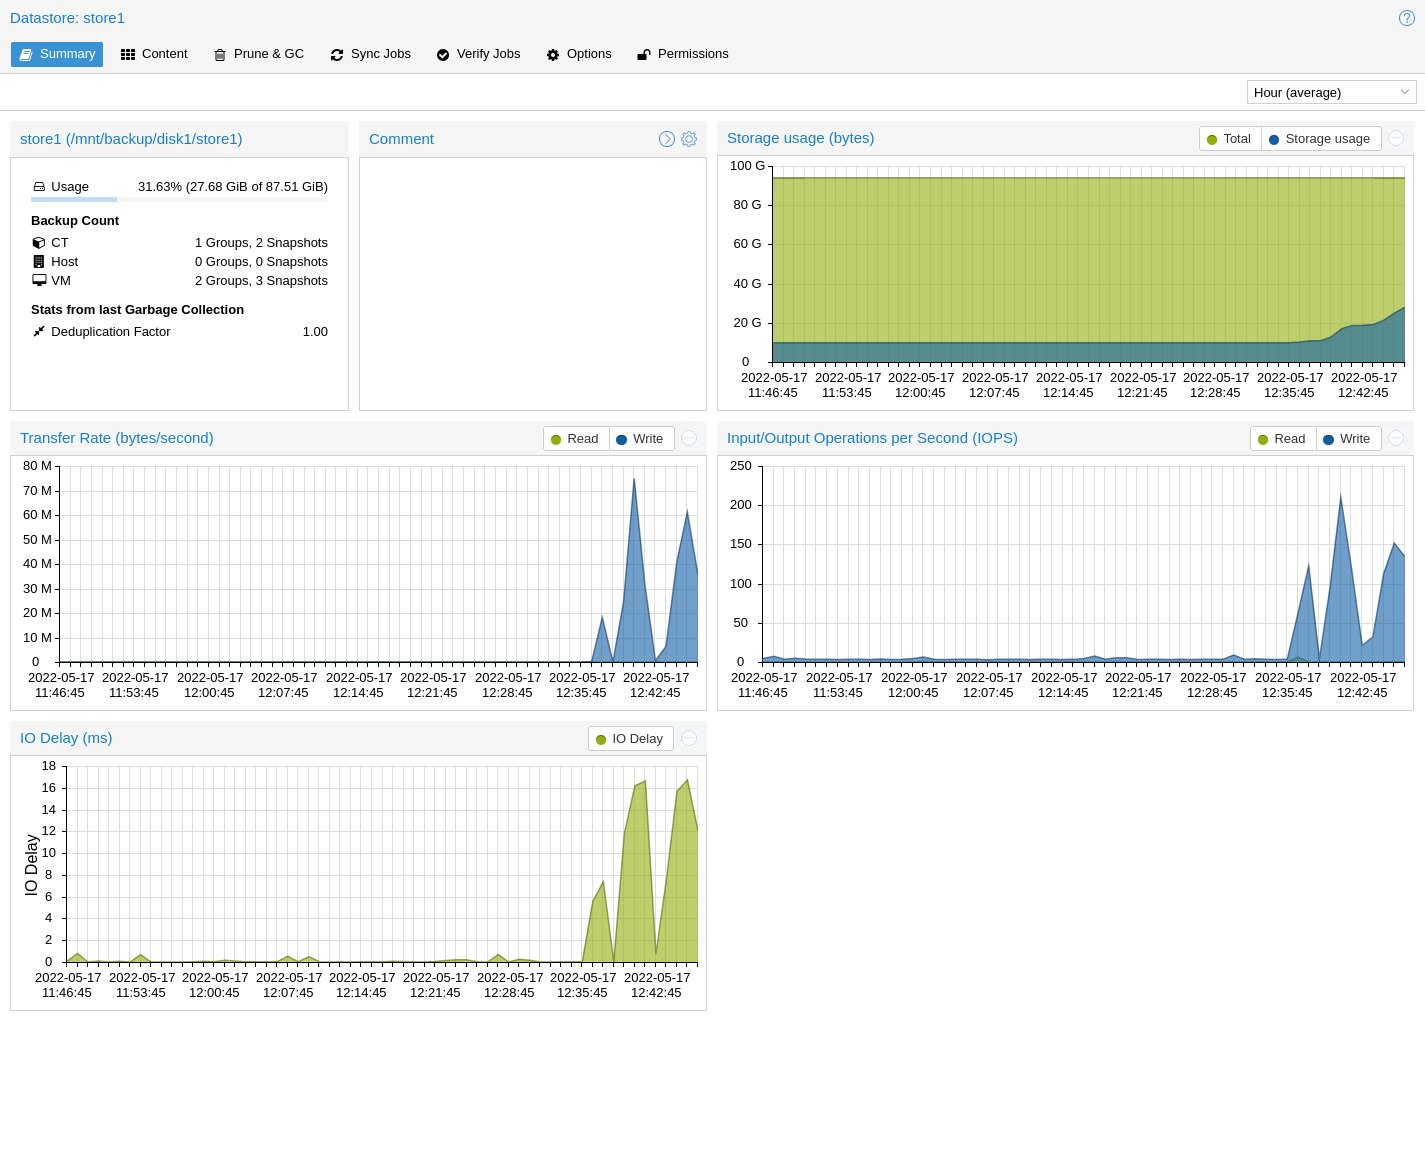
We keep two copy paths on separate accounts
Proxmox Backup Server or an equivalent path close to production, and a second path outside the site. Object lock, a separate key, a restore test. One cloud account is one path, the second path sits on another identity.
Path A
Close, short RTO
Snapshot and copy in the same location. Restore of system and application in a known time.
Path B
Far, separate identity
A second provider or tenant. A different key, a different network. This path does not use production accounts.
Scope
Databases, volumes, files, mail where it is a service, and IaC configuration.
Retention
Aligned with GDPR and the contract. Shortening retention is an alert, with an owner.
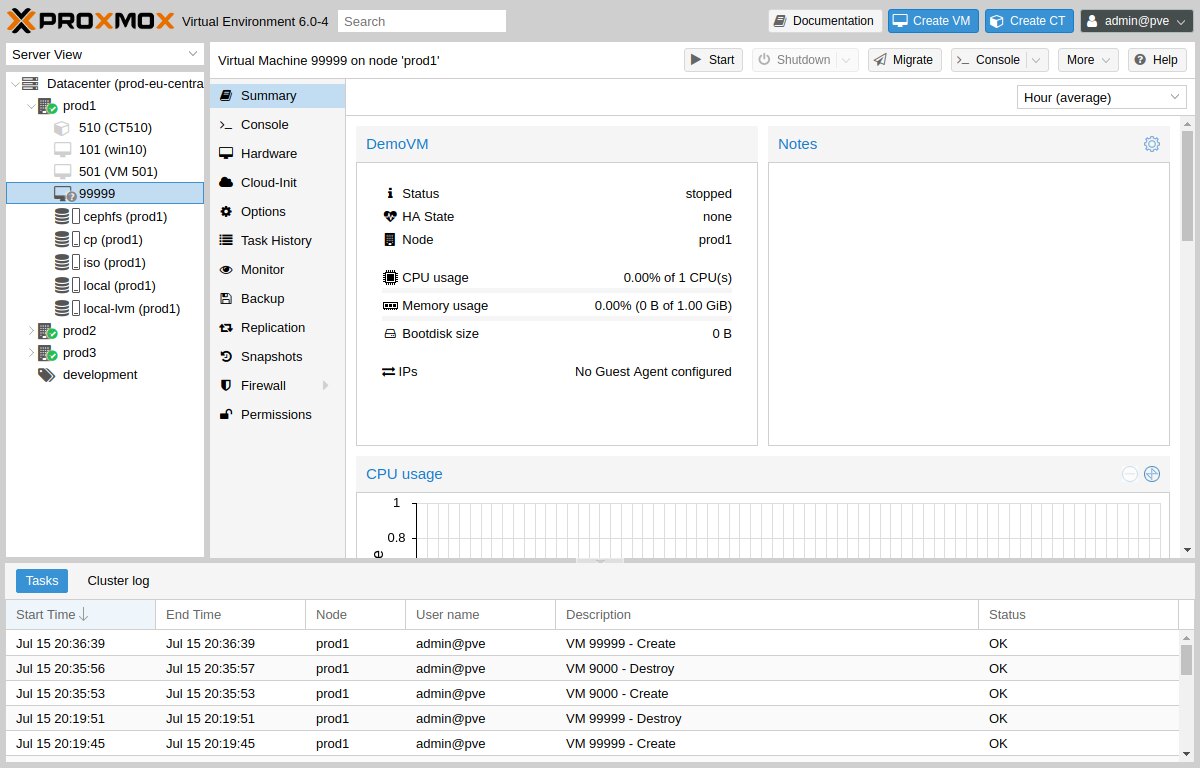
We protect disk and snapshot as a dataset too
On Proxmox and in the cloud a volume has encryption, a snapshot policy, and who may clone a disk. A VM template does not carry secrets. Test data is masked or synthetic.
Encryption
At rest and in transit. KMS or HSM, rotation, and separation of who uses and who administers the key.
Snapshot
Who may make a clone and where it lands. A snapshot is a copy, it falls under the same class.
Environments
Production feeds staging with a masked or synthetic dataset, when a full copy is not needed.
Deletion
Retention and the right to erasure have a procedure on backup, together with the application.
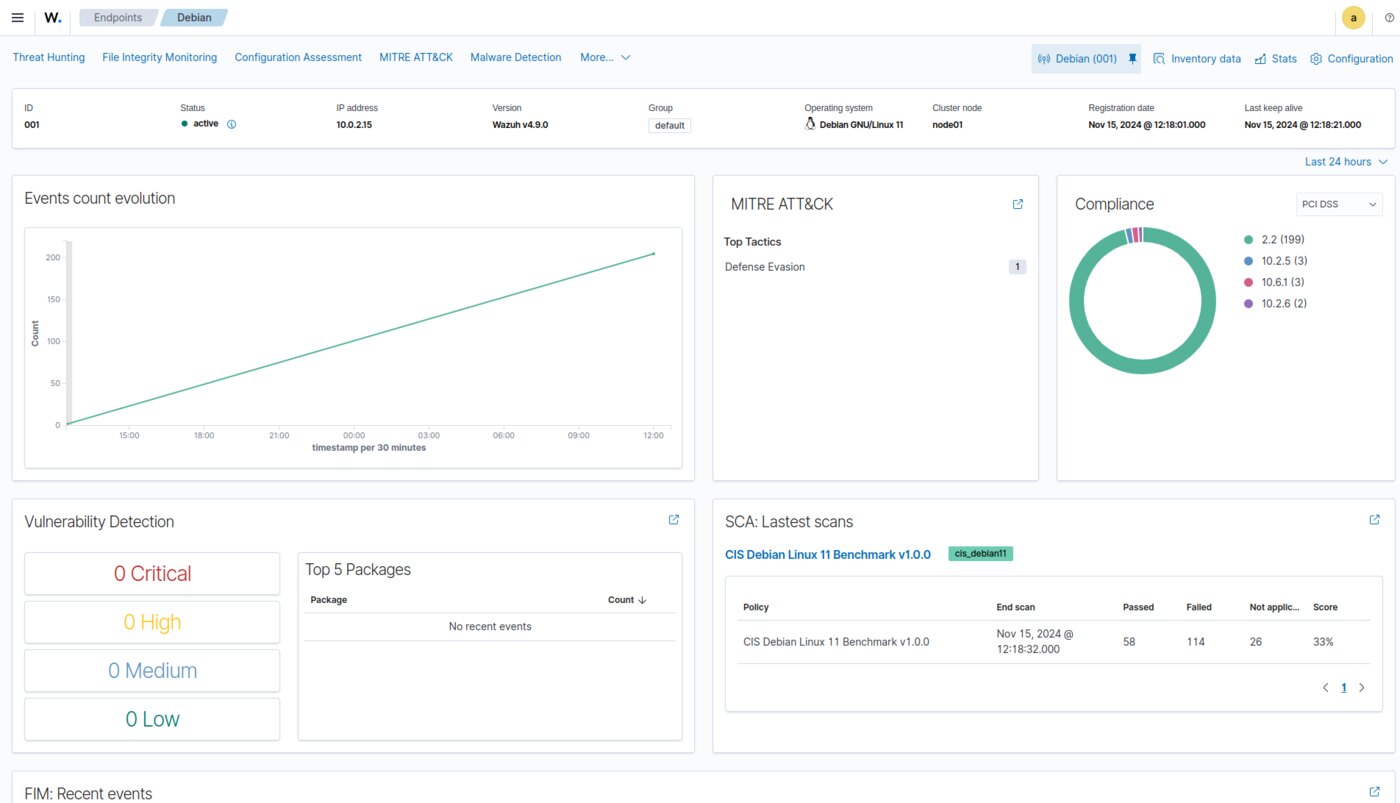
We watch who read a dataset and whether a file changed
FIM on data paths, access logs to the database and object storage, an alert on bulk download. This closes the server and the application. DLP on office endpoints stays a separate layer when you already have it.
FIM
Data directories, configuration, and keys. A change outside the window has priority.
Access
Login log, grant in the database, AssumeRole. An unusual hour and a new ASN go to on-call.
Exfiltration
Volume on egress, unusual destination. Correlation with traffic analysis where it is deployed.
Audit trail
Log retention for audit and a data subject request. Who saw the alert, what was done.
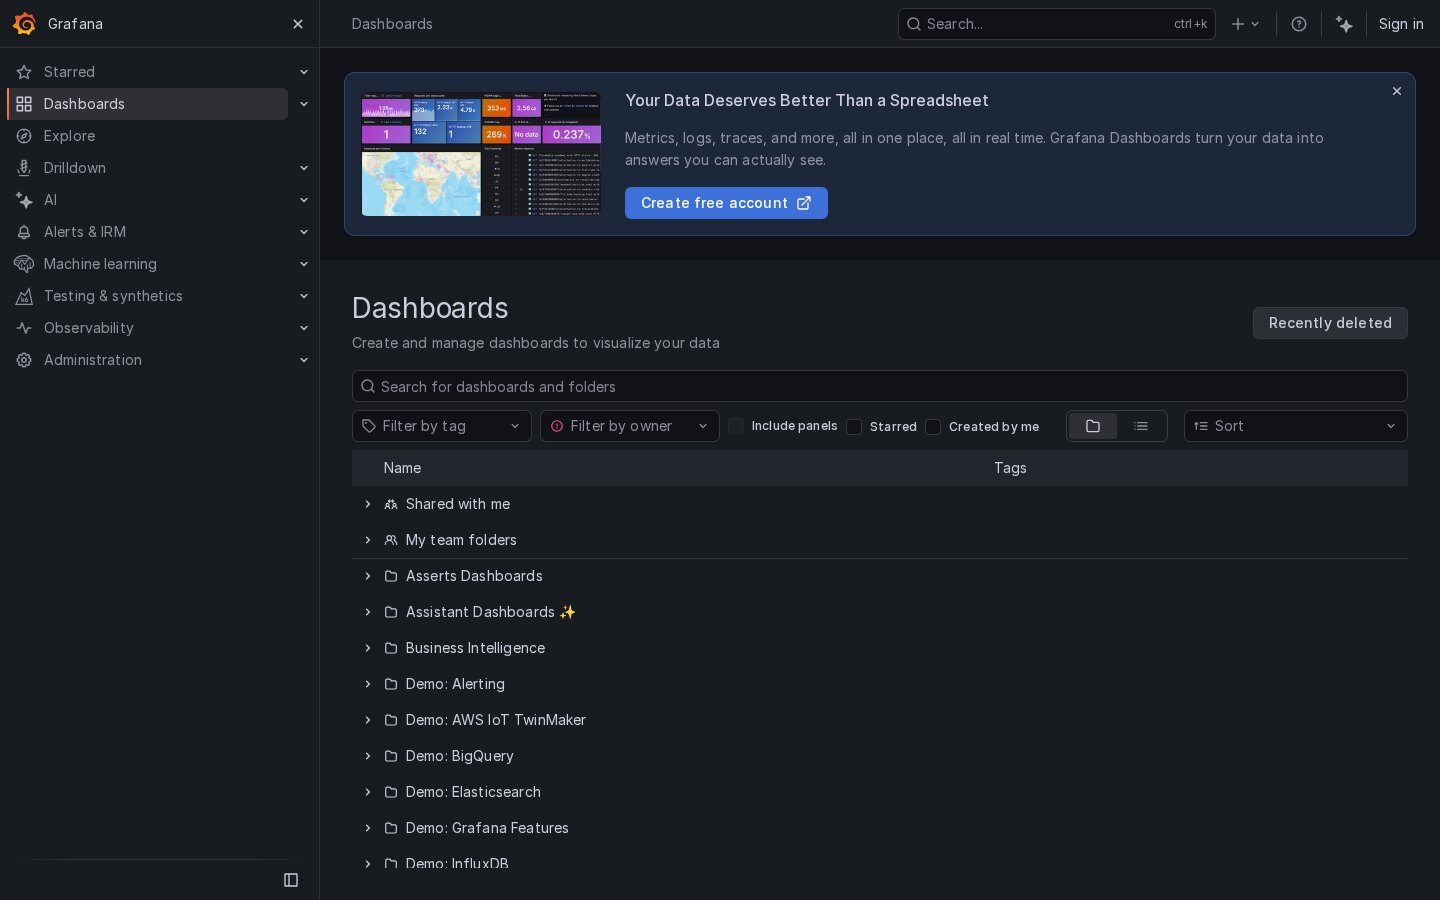
We keep backup, key, and retention on a chart
A failed copy job, a KMS error, an approaching certificate, rising egress. A dashboard for operations and material for the DPO, from the same status.
Backup
Success, time, volume, age of the last successful restore.
Keys
KMS use, decrypt error, attempt from an unknown account.
GDPR
Retention, deletion queue, request fulfillment time, written as a process metric.
People
DPO and engineering look at the same copy and access status, in a different language of description.
How we work
From the client datasets to a restore rhythm
We start from the inventory: datasets, classes, locations, who has the key, and which RPO. Then we stand up encryption, KMS, two copy paths, and FIM. We stay for GDPR requests, retention, and a report for the DPO.
- Inventory We check datasets, classes, locations, who has the key, and which RPO. That gives the scope: protection, copies, and rhythm.
- Protection We set encryption, KMS, staging masking, and clone restriction.
- Copies We stand up two paths, immutability, and a first successful restore.
- Rhythm We run FIM, GDPR requests, retention, and a report for the DPO. Restore stays on the calendar.
Talk
We will discuss the datasets, the keys, and restore
On that basis we will prepare a scope: protection, copies, and an audit trail.
Contact us