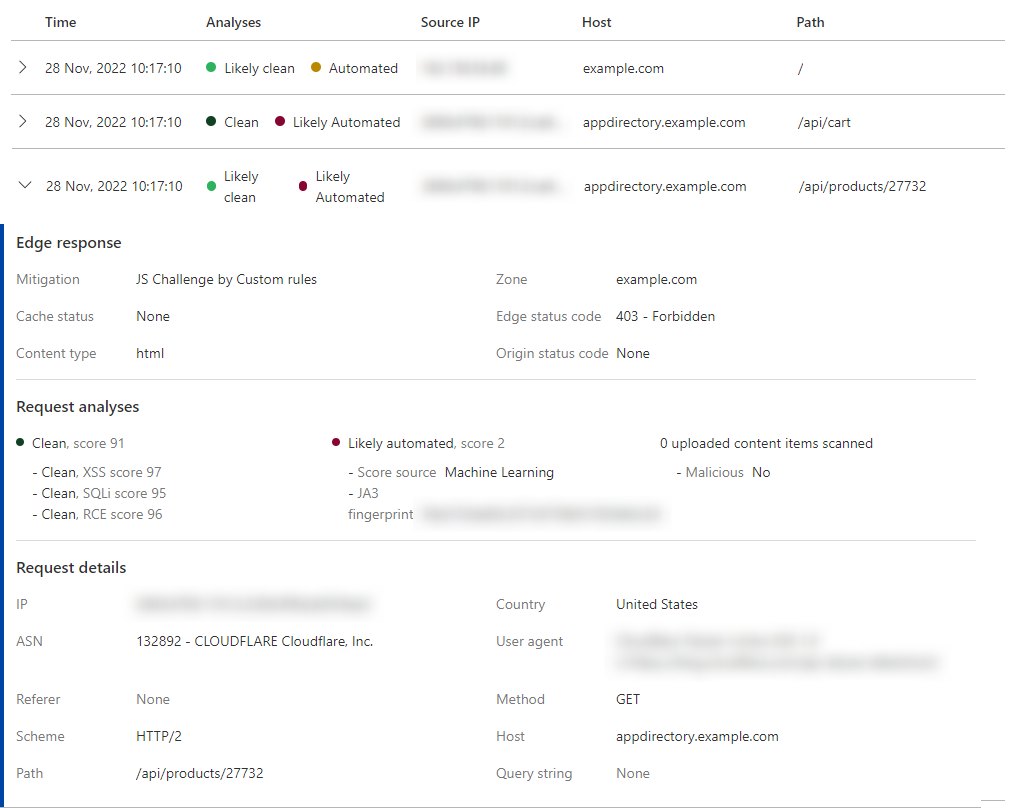
A bot does not have to look like a database attack. Often it is an ordinary hit on login, the cart or the product API, repeated from many addresses. In the store log you see a jump in errors. In Cloudflare you see the bot score and whether the edge issued a challenge or passed the request to the server.
Bot score and challenge
We start with a map of paths: login, cart, search, payment webhooks. Verified bots, search and monitoring, stay allowed. Traffic with a low score gets a challenge or a block. The store server has no public address. DNS and encryption end at the edge.
A rule without context breaks checkout. That is why we look at sampled logs, not only the chart. If the challenge catches real customers behind a corporate proxy, we narrow the condition to the path, not the whole hostname.
Origin off the internet
The outcome can be billed: fewer attempts on login, the same cart response time, fewer surprises at the payment gateway. On-call knows when to raise the threshold and when to leave the challenge. The same layers are in infrastructure security and ecommerce operations.
In short: the edge scores traffic before it reaches PHP. The store server does not have to hang on the internet. A rule that also cuts payments is worse than no rule.