A store fails either on bots or on its own peak. Card and password attempts hit login and payment. Scraping cleans stock. An injected script waits on origin. A campaign adds traffic nobody will tell from an attack if there is no baseline map of flows.
Edge and cart
At the edge: Cloudflare on the store hostname and API. A request limit on login and checkout. Bot score on paths that are not a payment webhook. The store server without a public address. WAF does not replace patching Magento. It cuts the mass before it reaches PHP and the database.
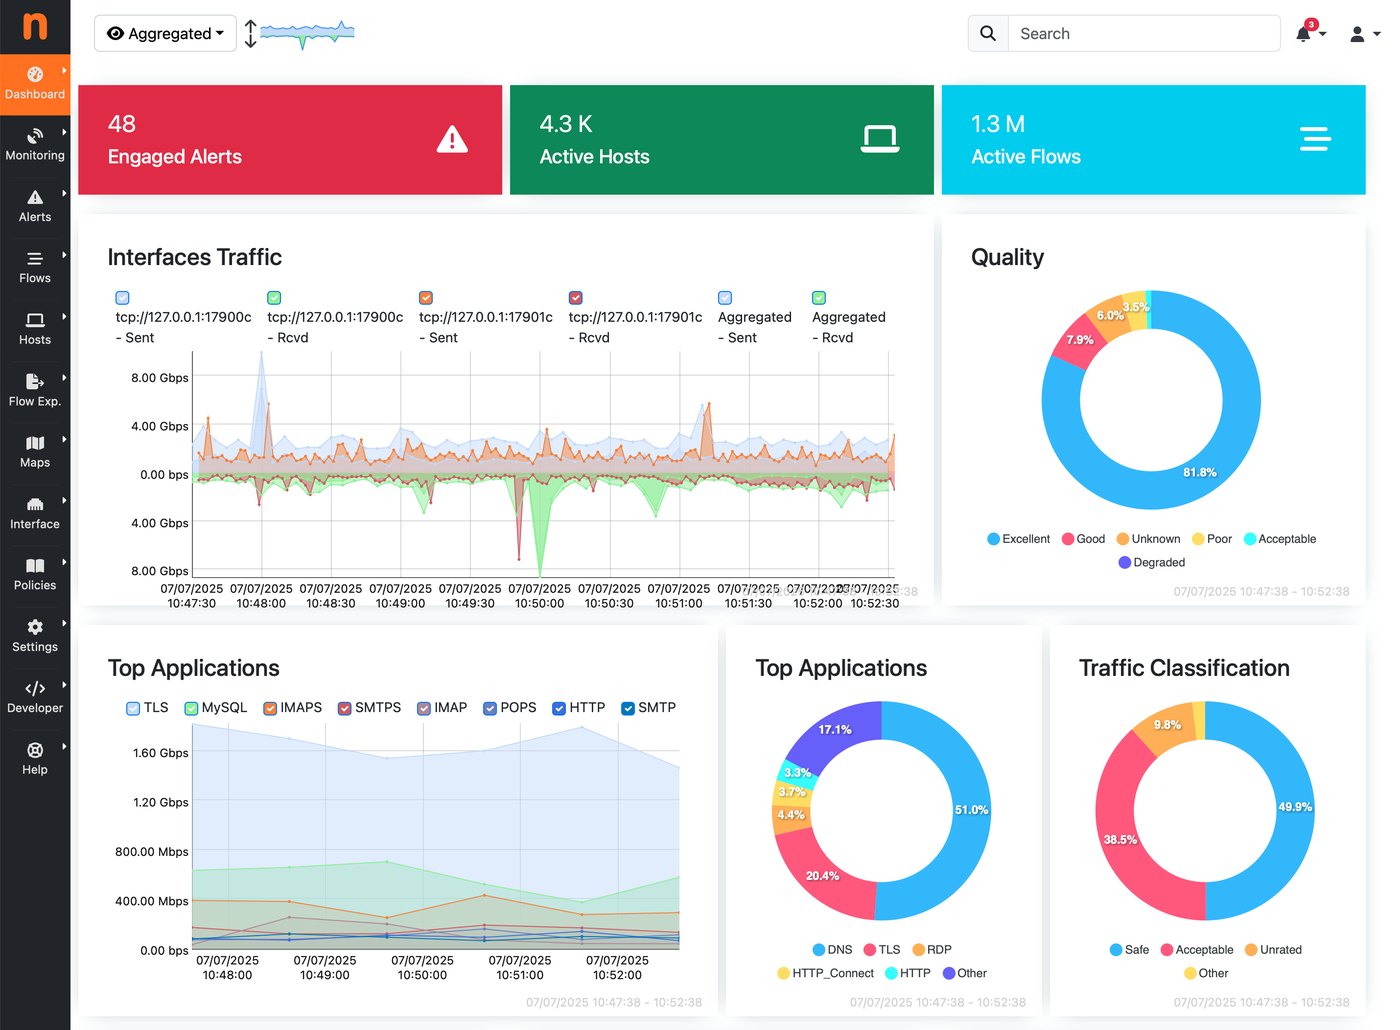
On the network, a view of hosts and applications says whether the jump is customers or a scan. The same picture goes to on-call together with Cloudflare and Wazuh on store, database and panel hosts.
A test before the season
Before the peak we test the cart path, not the homepage. Then change windows are closed, the copy is checked, and the playbook says who raises the challenge, who scales, who pauses the campaign. Ecommerce protection is these layers together, not a certificate on the storefront. Scope: ecommerce and load testing.
In short: before the season you know how the cart looks under load and how to tell customers from a scan. A TLS certificate does not cover that.